Fortigate with IPSEC and SAML auth.
If the fortigate have VDOM enabled
config global
    config system global
        set auth-ike-saml-port 10428
    end
endCode language: PHP (php)
If not
config system global
    set auth-ike-saml-port 10428
endCode language: JavaScript (javascript)
The rest should be in the VDOM where the vpn connection will terminate
config firewall address
    edit "dialup_ipsec_range"
        set type iprange
        set comment "VPN: dialup_ipsec"
        set start-ip 10.1.1.1
        set end-ip 10.1.1.254
    next
end

config vpn certificate remote
    edit "EntraID-SSO-PVE-DevOps"
        set remote "-----BEGIN CERTIFICATE-----
MIIC8DCCAdigAwIBAgIQYdenK6B+Ab1JW2l9N3GFmzANBgkqhkiG9w0BAQsFADA0
MTIwMAYDVQQDEylNaWNyb3NvZnQgQXp1cmUgRmVkZXJhdGVkIFNTTyBDZXJ0aWZp
Y2F0ZTAeFw0yNjAzMjUxNTE4NDNaFw0yOTAzMjUxNDE4NDFaMDQxMjAwBgNVBAMT
KU1pY3Jvc29mdCBBenVyZSBGZWRlcmF0ZWQgU1NPIENlcnRpZmljYXRlMIIBIjAN
MIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEAt7R9lP4D2YQbVnQ8WgFs
8h2NcYk5bZg7rQdU6Kx3PnL0sEtV5Zc4JmN9QhAwLrYkFp2sUv6wCeD8eKtJxTqA
yM4iBr5GnF2vQ9ZL7TzK8hYVnL4dA6PfJc9Xw2RsGm7KeY1FzBtVn8hQm5LpRcUa
c3Ew8NqJvL1YsG6PdX2mAr7Vt9FwKjQ5sNcUyLhA0xPeVr7CmQd8KjXyYvL3oA1N
kR8tDzW4GmLpHs7NcJvQeY3mPwL2ZxFhB5UcRtN6KqYjM8VpXeC4FgQ9LtPwDmYh
XvL8AnKj3JmPt5YwQh7VcF2LzNgEr6PsJxUw9VhQ2BnKmL4XtD3FwQIDAQABMA0G
CSqGSIb3DQEBCwUAA4IBAQAfXzL8YkQv9N6eWpJ2FhA0RtCmX7uQdM4PnL8JkV3R
sY6NwPfHtL2jCm8QxVrE7dF5KtVbA1yM9cGhLq2FwX8rQzUvNdE5LmHkP7BaX9sT
uK1yJvH4QwMtLx3PeZ7GfQ8VdJm2NrTwYkL5AsXrPn8MbCtHqV6LwReZ3YsQfG7X
nD5PtVjQmL8ZxHsRaC4WkF2YpN7eUtMqJv9BxLgRdK3HwTsYpV4FmNcQ8ErLzJdA
gY7kMvPt2QxLcHsFwK8NeYv3JmRtP5UaDxLqZ9WcBnE8GtHsX2PvKrQmL5NfY7Zt
SBVNTS/V41ZJTfvL/njgrKES5SxxvHO/d/OGbqb7dbx1riZN
-----END CERTIFICATE-----"
    next
end

config user saml
    edit "Demo-EntraID"
        set entity-id "http://vpn.test.scito.dk:10428/remote/saml/metadata/"
        set single-sign-on-url "https://vpn.test.scito.dk:10428/remote/saml/login"
        set single-logout-url "https://vpn.test.scito.dk:10428/remote/saml/logout"
        set idp-entity-id "https://sts.windows.net/11111111-2222-3333-4444-555555555555/"
        set idp-single-sign-on-url "https://login.microsoftonline.com/11111111-2222-3333-4444-555555555555/saml2"
        set idp-single-logout-url "https://login.microsoftonline.com/11111111-2222-3333-4444-555555555555/saml2"
        set idp-cert "EntraID-SSO-PVE-DevOps"
        set user-name "username"
        set group-name "http://schemas.microsoft.com/ws/2008/06/identity/claims/groups"
        set digest-method sha1
    next
end

config system interface
    edit "WAN"
        set ike-saml-server "Demo-EntraID"
    next
end

config user group
    edit "sec_pvedevops"
        set member "Demo-EntraID"
        config match
            edit 1
                set server-name "Demo-EntraID"
                set group-name "11111111-222229-33333-44444-555555555"
            next
            edit 2
                set server-name "Demo-EntraID"
                set group-name "sec_pvedevops"
            next
        end
    next
end

config vpn ipsec phase1-interface
    edit "dialup_ipsec"
        set type dynamic
        set interface "WAN"
        set ike-version 2
        set peertype any
        set net-device disable
        set mode-cfg enable
        set proposal aes256-sha256 aes128-sha256
        set dhgrp 21 20
        set eap enable
        set eap-identity send-request
        set authusrgrp "sec_pvedevops"
        set assign-ip-from name
        set dns-mode auto
        set ipv4-name "dialup_ipsec_range"
        set save-password enable
        set client-keep-alive enable
        set psksecret ENC <REDACTED_ENCRYPTED_PSK>
    next
end
end

config vpn ipsec phase2-interface
    edit "dialup_ipsec"
        set phase1name "dialup_ipsec"
        set proposal aes256-sha256 aes128-sha256
        set dhgrp 21 20
        set keepalive enable
    next
end
Code language: JavaScript (javascript)
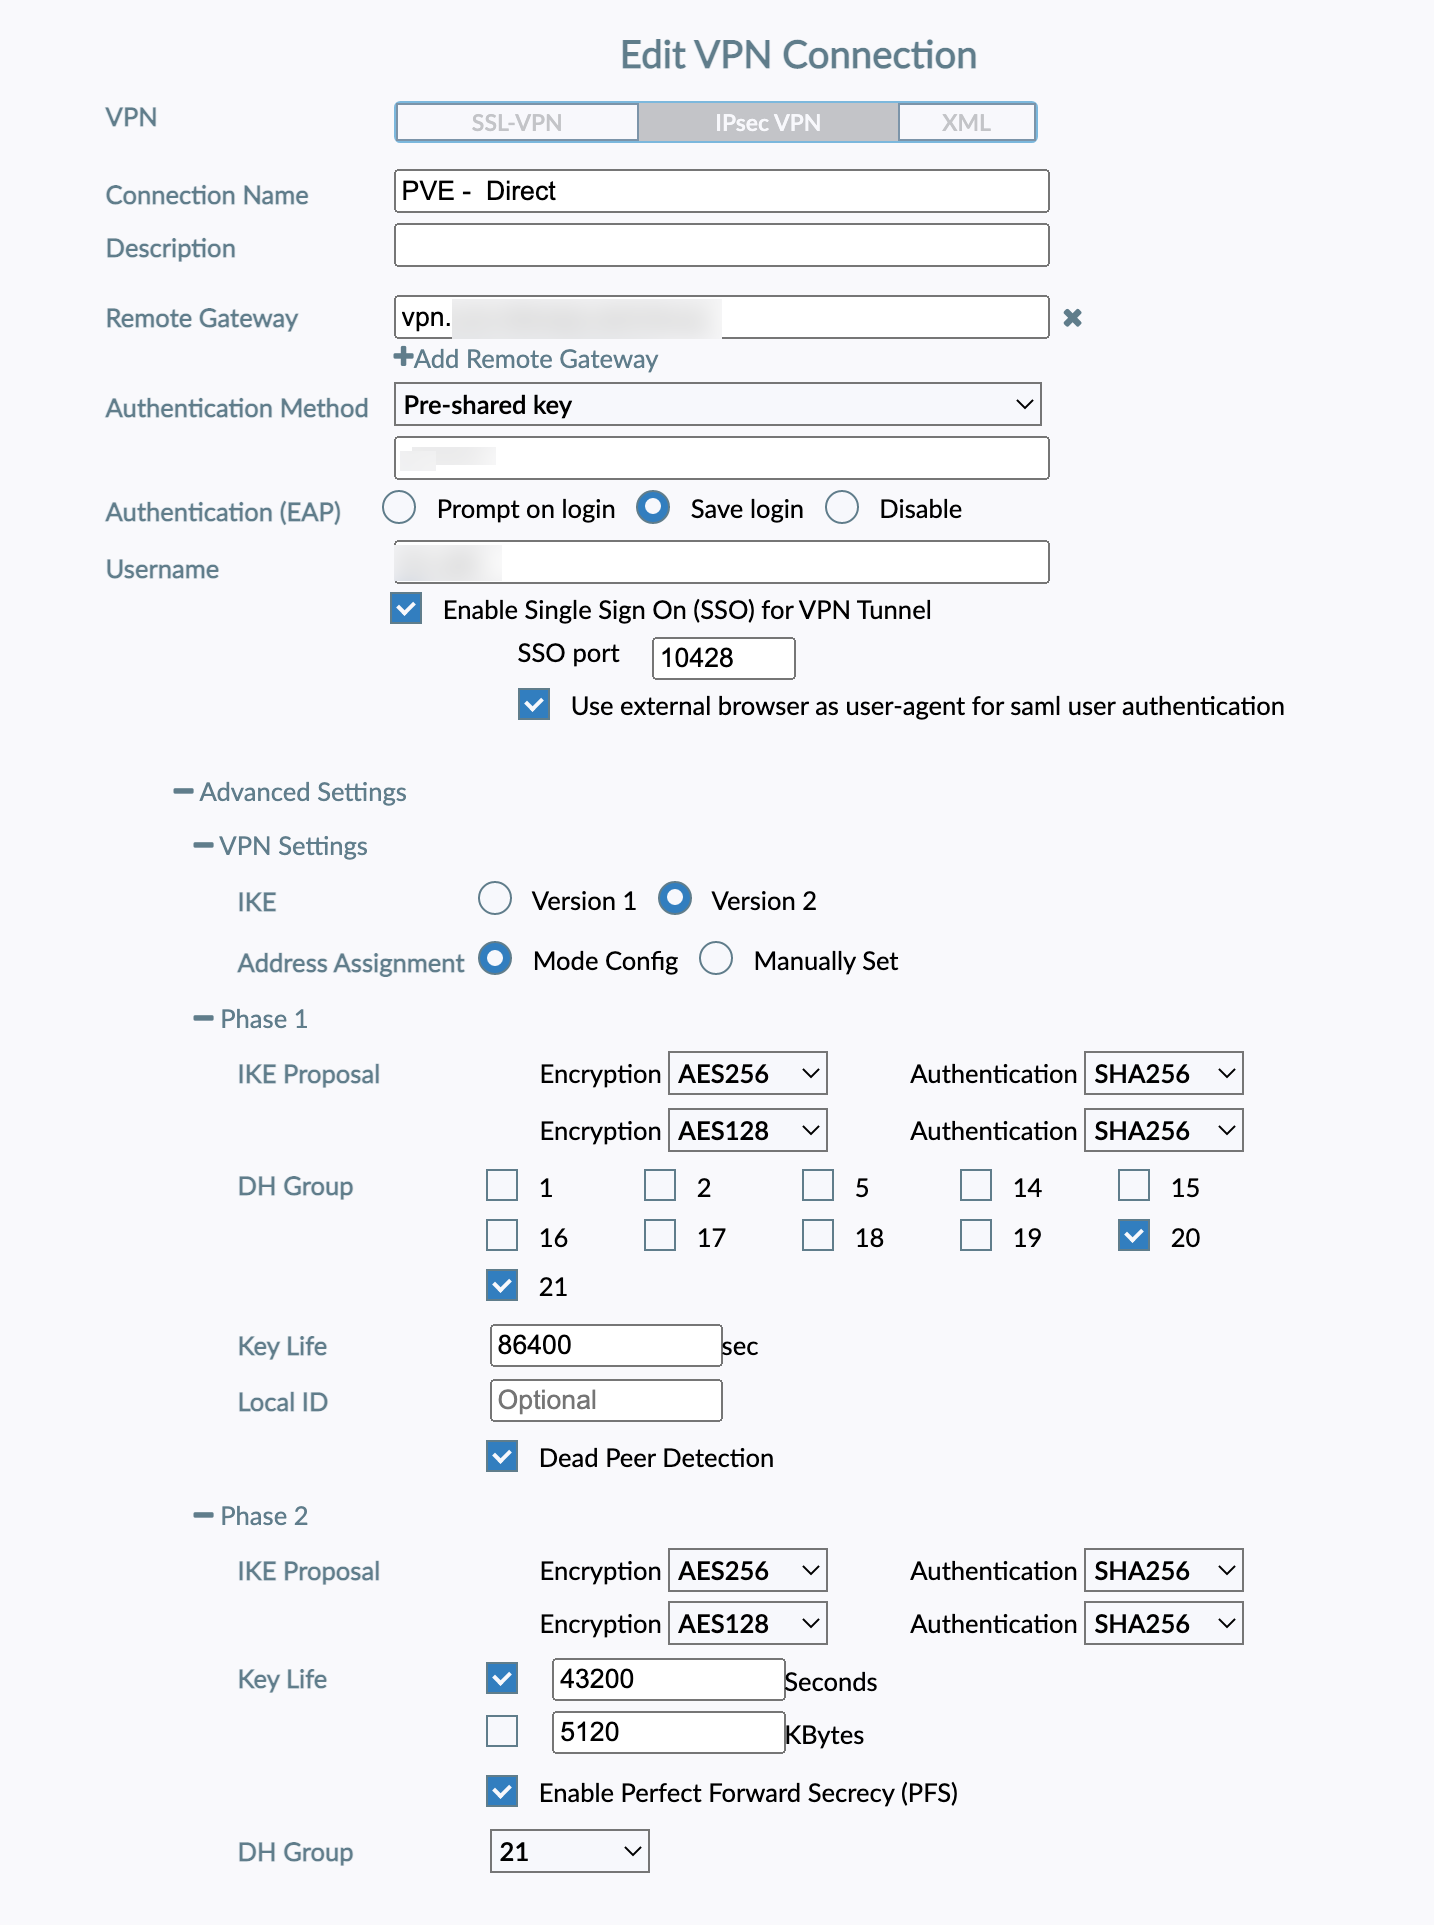
Forticlient like this